Limited early access
Android only
An AI pentester for mobile apps
An AI pentester
for mobile apps that
An AI pentester for mobile apps
Get only confirmed security findings! Let AI Pentester trace untrusted data through your code, simulate attacks, and execute exploits in a running app.
Built on real security research, not LLM guesswork
Built on real security research, not LLM guesswork
Built on real security research, not LLM guesswork
We're onboarding a few mobile security teams at a time, so that each one gets direct support from the researchers who built it.
We're onboarding a few mobile security teams at a time, so that each one gets direct support from the researchers who built it.
We're onboarding a few mobile security teams at a time, so that each one gets direct support from the researchers who built it.
1
1
Contact our team
Tell us about your app and
what your current testing misses
Tell us about your app and
what your current testing misses
2
2
We send you the steps
Learn how to share your build and
set up test accounts
Learn how to share your build and
set up test accounts
3
3
You get proven findings
Full code execution, triggered
by loading a web page
Full code execution, triggered
by loading a web page
See all your apps
and teams in one workspace
See all your apps and teams in one workspace
See all your apps
and teams in one workspace
Built on years of mobile security research by Sergey Toshin
and hundreds of real-world application tests.
Built on years of mobile security research by Sergey Toshin and hundreds of real-world application tests.
AI reasoning
AI reasoning
Investigates attack path
and builds exploits
Investigates attack path
and builds exploits
Proprietary taint analysis
Proprietary taint analysis
Traces untrusted data through your app to vulnerable code
Traces untrusted data through
your app to vulnerable code
Traces untrusted data through your
app to vulnerable code
6,000+ custom rules
6,000+ custom rules
Built on years of mobile security research
Built on years of mobile
security research
Runtime exploit validation
Runtime exploit validation
Tests exploits in a running app to confirm each finding
Tests exploits in a running app
to confirm each finding
Tests exploits in a running app to
confirm each finding
AI pentester features
AI pentester features
AI pentester features
Eliminate false positives
Get confirmed findings instead of spending hours manually validating scanner alerts
Test beyond the login screen
Automatically authenticate and investigate protected flows, including payments, accounts, and sessions
Connect vulnerabilities into attack chains
Uncover how separate weaknesses can be combined into real-world attacks
Get developer-ready reports
Every finding comes with reproduction steps, PoCs, stack traces, screencasts, CVSS scores, and clear business impact
Pentest whenever you need to
Run autonomous security tests on demand, without scheduling external pentesters or waiting months

Stay on top of compliance
Test against 268 vulnerability categories mapped to 53 standards and regulations, including OWASP MASVS, PCI DSS, DORA, GDPR, NIS2, and HIPAA
Eliminate false positives
Get confirmed findings instead of spending hours manually validating scanner alerts
Test beyond the login screen
Automatically authenticate and investigate protected flows, including payments, accounts, and sessions
Connect vulnerabilities into attack chains
Uncover how separate weaknesses can be combined into real-world attacks
Get developer-ready reports
Every finding comes with reproduction steps, PoCs, stack traces, screencasts, CVSS scores, and clear business impact
Pentest whenever you need to
Run autonomous security tests on demand, without scheduling external pentesters or waiting months
Stay on top of compliance
Test against 268 vulnerability categories mapped to 53 standards and regulations, including OWASP MASVS, PCI DSS, DORA, GDPR, NIS2, and HIPAA
Get a bug bounty-style report
for every finding
Get a bug bounty-style report
for every finding
Most scanners tell you a vulnerability exists. Oversecured agents tell you what it means, how severe it is, and exactly how to fix it in language your developers can act on.

Business impact
What an attacker could achieve if this is exploited: data theft, account takeover, financial loss

Technical impact
What happens at the system level: which data is exposed, which operations are affected

Proof of Concept
Full command, deeplink payload, or exploit code to reproduce the issue
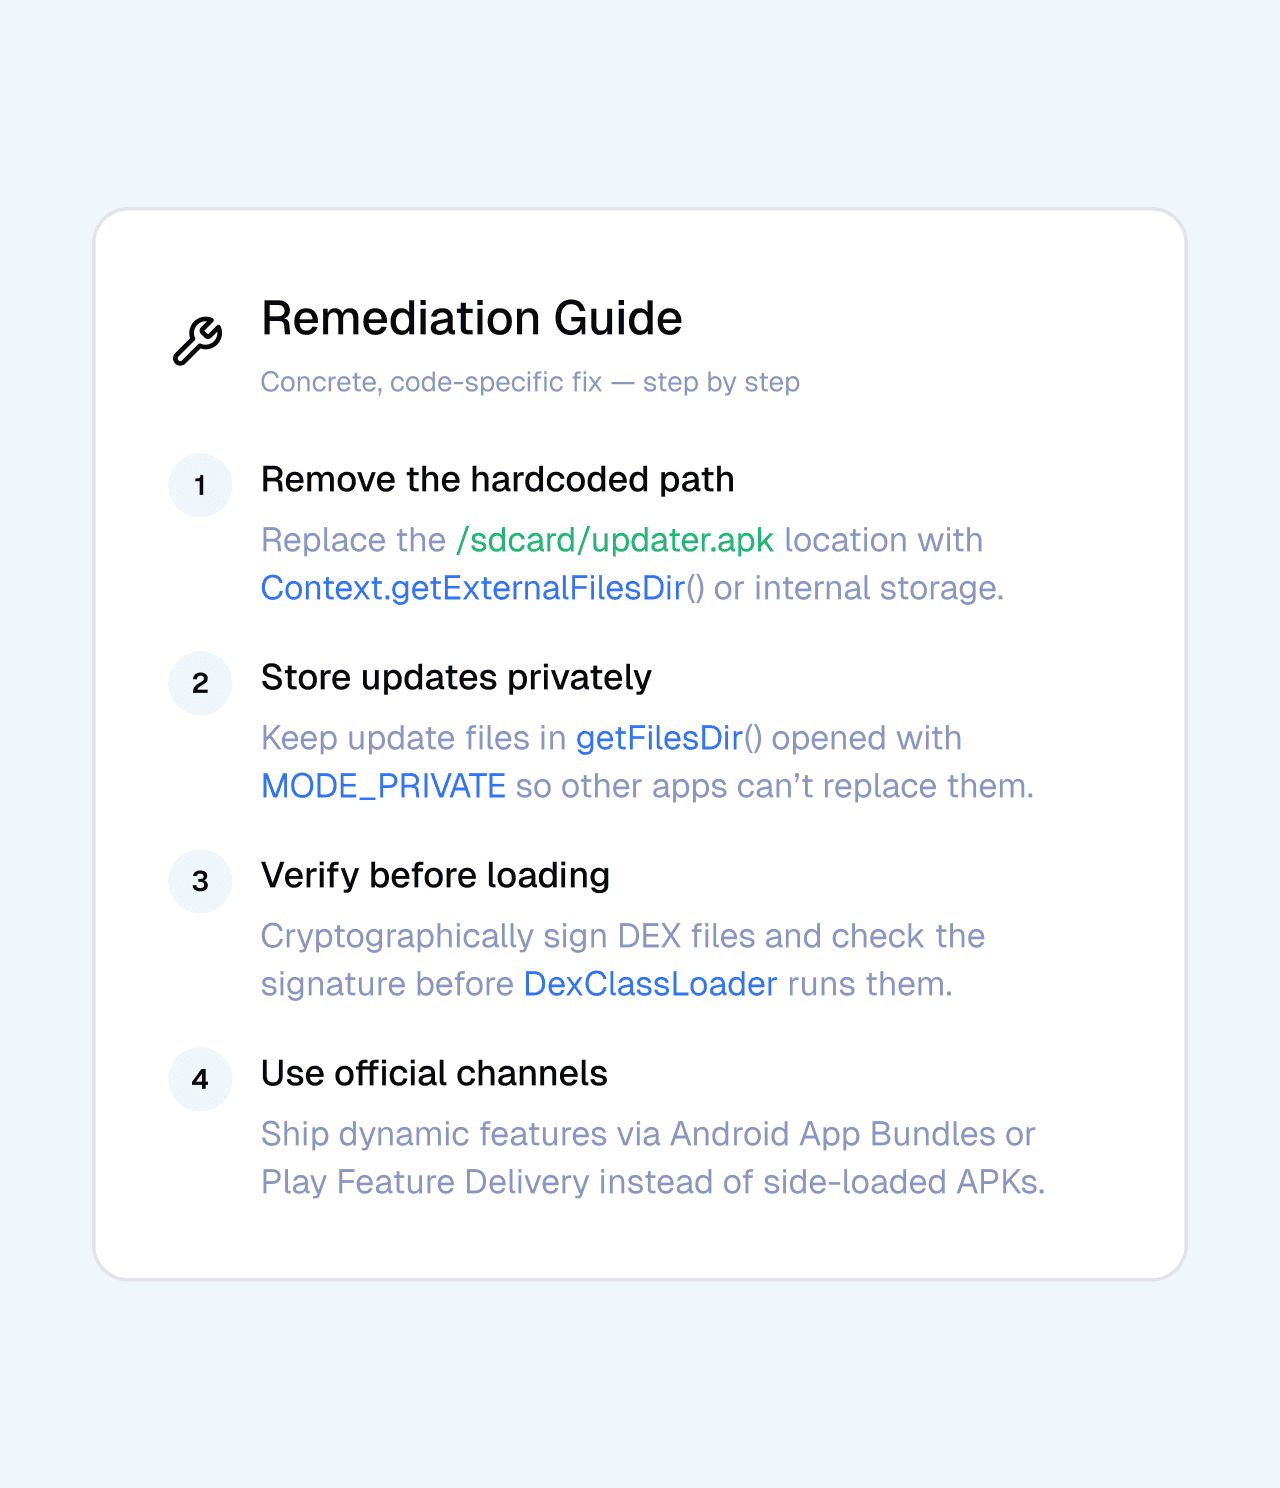
Remediation Guide
Concrete remediation guidance, specific to the code and context — not a generic reference to a standard

Agent Reasoning
See the step-by-step chain of thoughts to understand how the agent found the vulnerability

Code snippet
The relevant lines of code, highlighted

Stack trace
The full execution path of the code

Screencast
The video recording of an emulator showing the vulnerability in action
Early access spots
are limited
Early access spots
are limited
Tell us about your app. Our team will reply
with the steps to run your first test
Start a free trial and see taint analysis, authenticated scanning, and exploit-backed checks in action.
Get a bug bounty-style report for every finding
Most scanners tell you a vulnerability exists. Oversecured agents tell you what it means, how severe it is, and exactly how to fix it in language your developers can act on.

Business impact
What an attacker could achieve if this is exploited: data theft, account takeover, financial loss

Technical impact
What happens at the system level: which data is exposed, which operations are affected

Proof of Concept
Full command, deeplink payload, or exploit code to reproduce the issue

Remediation Guide
Concrete remediation guidance, specific to the code and context — not a generic reference to a standard

Agent Reasoning
See the step-by-step chain of thoughts to understand how the agent found the vulnerability

Code snippet
The relevant lines of code, highlighted

Stack trace
The full execution path of the code

Screencast
The video recording of an emulator showing the vulnerability in action